Lesson 5 of 63
Journey A, part 5: The Data Protection Officer reviews the answers
What you will be able to do
The supplier has answered. In this part the Data Protection Officer reads the risk score, checks the answers and the certificate, records one gap as a finding with an owner and a due date, and asks a second Data Protection Officer to approve. The preparer cannot approve their own review.
Before you start
- Part 4 is done: the supplier submitted its answers.
- You are signed in as the Data Protection Officer who sent the questionnaire.
Steps
- 1
Find the supplier that has answered
Open Data Protection, then Vendor risk. The supplier's row now shows To review under Latest assessment, and the To review tile counts it. Select the supplier's name.
- 2
Open the supplier's page
The supplier's page shows its risk status, its details and its inherent risk. Under Assessment history the newest questionnaire is at the top, with a Review link.
- Select Najm Al Sahra Fulfilment LLC
- 3
Select Review and read what to do next
Select Review. The box at the top always says what happens next and holds the buttons for it: recalculate the score, raise a finding, return the questionnaire to the supplier, or request approval.
- Select Review
- 4
Read the risk score and tier
Inherent risk is the risk before safeguards, out of one hundred. Control score is how well the supplier's answers show it protects the data. Residual risk is what is left, and it sets the tier: Low, Medium, High or Critical. The line underneath shows the calculation.
- 5
Check the certificate the supplier attached
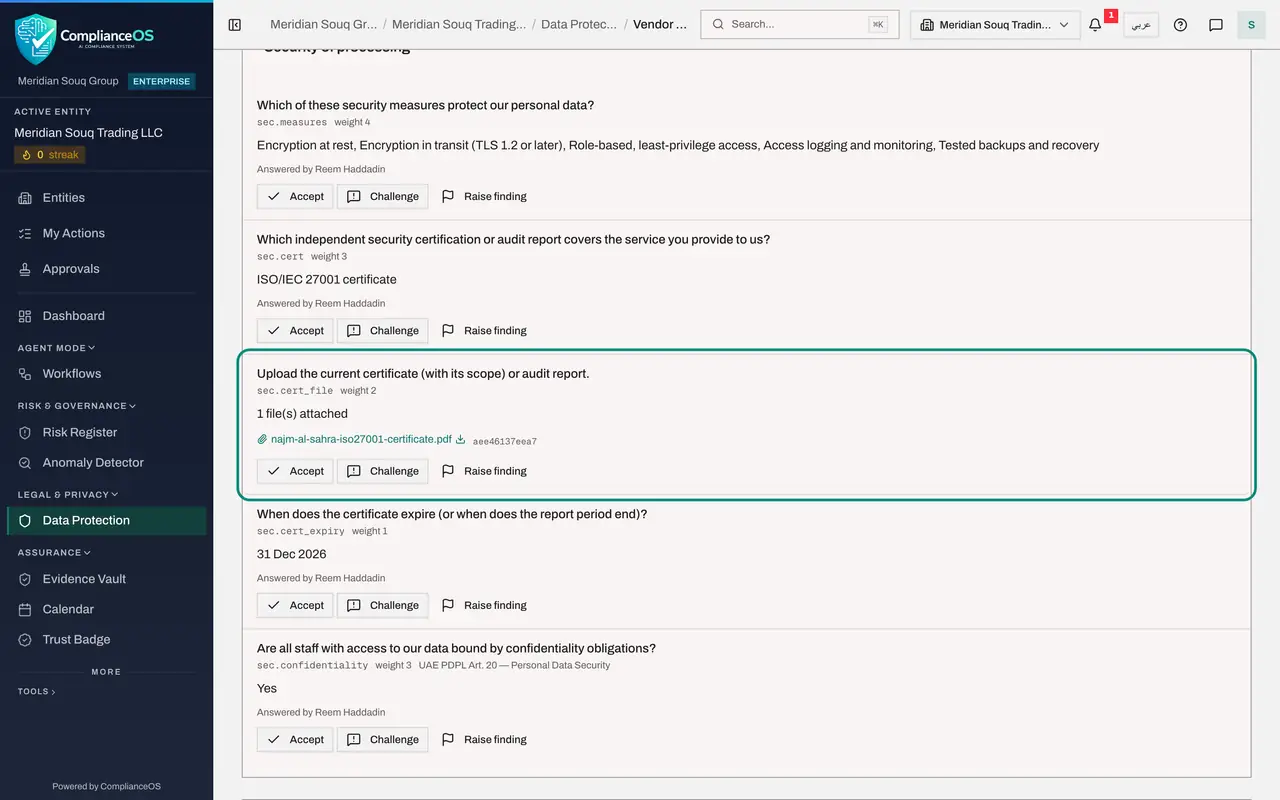
Scroll down to Answers. Each question shows the supplier's answer, who gave it, and any file attached. Find the certificate upload. Select the file name to download it, and check that it is current and covers the service you use.
- 6
Accept an answer you are satisfied with
The supplier will report a breach within 24 hours, which matches the contract. Select Accept on that answer and it is marked Accepted. If an answer needed correcting, you would select Challenge and say what the supplier should change.
- Select Accept
- 7
Raise a finding on the expiry date
The certificate expires on 31 December 2026, only weeks away. On the expiry date answer, select Raise finding. A finding records a gap and the action needed to close it.
- Select Raise finding
- 8
Describe the finding, its owner and due date
Give the finding a short title and say why it matters. In Owner, name the person who will follow it up. Set a due date, and under Remediation action write what the supplier must do.
- Type Finding:
Security certificate expires in December 2026 - Type Details:
The ISO 27001 certificate expires on 31 December 2026, during the cont… - Type Owner:
Head of Logistics - Type Due date:
2027-01-12 - Type Remediation action:
Send the renewed ISO 27001 certificate as soon as it is issued.
- Type Finding:
- 9
Save the finding
Select Save. The finding is listed at the bottom of the page as Open. It also appears under the Findings tab of Vendor risk, where every supplier's findings are tracked together.
- Select Save
- 10
Select Request approval
Go back to the top and select Request approval. The status changes to Waiting for approval. A second person must now decide: whoever prepared the review cannot approve it. That is the next part, for Najm Al Sahra Fulfilment LLC's second reviewer.
- Select Request approval
How to check it worked
The assessment says Waiting for approval, and the finding is listed as Open with its owner and due date. In the next part your colleague approves.
Common mistakes
- Asking for approval without opening the evidence. The certificate's dates and scope are the proof behind the answers.
- Raising a finding with no owner or due date. Nobody follows up a gap that belongs to no one.
- Trying to approve your own review. The approval must come from a second person.
Check your understanding
1. What sets the supplier's risk tier?
- A.The residual risk: inherent risk reduced by the control score
- B.The contract value
- C.The number of questions answered
Show answer
Answer: A. The residual risk: inherent risk reduced by the control score
Inherent risk is the risk before safeguards; the answers give a control score; what is left is the residual risk, which sets the tier.
2. The certificate the supplier uploaded expires in ten weeks. What do you do?
- A.Reject the whole questionnaire
- B.Raise a finding with an owner and a date to obtain the renewed certificate
- C.Ignore it; it is valid today
Show answer
Answer: B. Raise a finding with an owner and a date to obtain the renewed certificate
A finding records the gap and the action to close it, and stays on the supplier until it is closed.